Blog

How to Build an Effective Supply Chain Governance Strategy

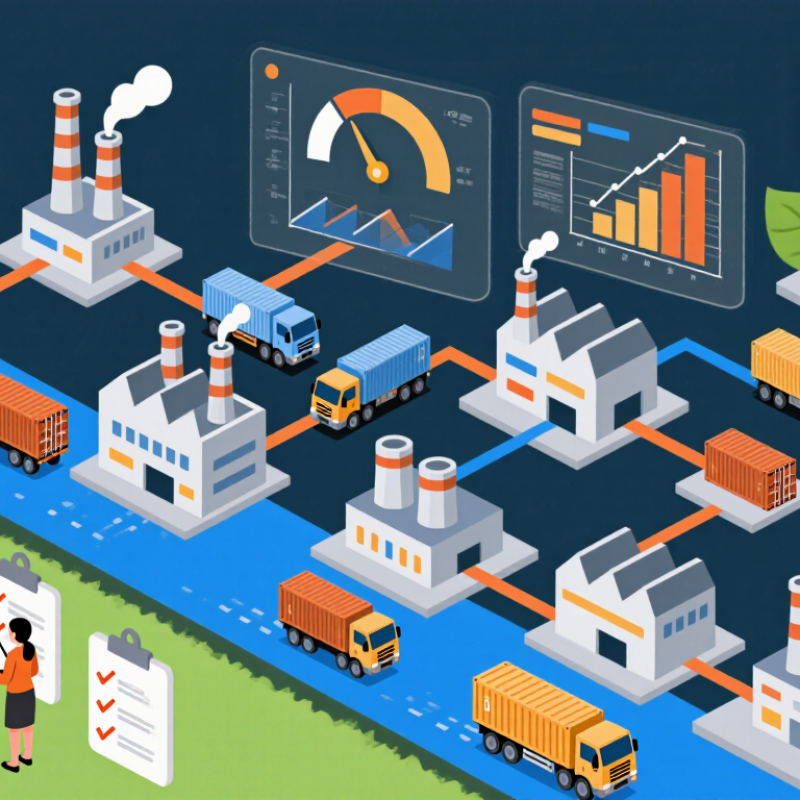
Supply Chain Governance is the operating discipline behind reliable, ethical, and resilient supply networks. It defines who makes decisions, how risks are reported, and which standards suppliers must meet. A practical strategy connects procurement, logistics, finance, compliance, and operations through clear accountability. Without that connection, a delayed shipment can become a production stoppage within hours.

Good governance begins with a visible map of the supply chain. Identify critical suppliers, single-source materials, transport dependencies, and data owners. Then establish measurable controls for quality, delivery, cybersecurity, environmental performance, and responsible sourcing. Supplier scorecards should use evidence, such as inspection records, delivery variance, corrective-action closure, and audit results. Standards such as ISO 9001 and ISO 28000 can provide useful reference points, but they should not replace sound judgment.

People must know what happens when a target is missed. A weekly review may examine a red supplier score, a container held at port, or an unexplained invoice change. These details make governance operational rather than decorative. Independent audits and documented escalation paths strengthen credibility, especially when commercial pressure encourages shortcuts. Still, no framework is perfect. Some risks remain hidden, and a polished dashboard can create false confidence. Leaders should test assumptions, invite uncomfortable feedback, and revise controls after failures. That reflective habit supports dependable decisions across changing markets, supplier relationships, and customer expectations. Good governance is not a one-time project. It is a practiced capability.
How to Build an Effective Supply Chain Governance Strategy

Define the Purpose and Scope of Supply Chain Governance

An effective supply chain governance strategy begins with a precise purpose. It should explain why decisions need shared rules, not simply add another approval layer. The 2023 MHI Annual Industry Report found that 74% of surveyed supply chain professionals planned to invest in innovation. Governance must therefore guide investment, risk, data, and accountability. Without clear intent, technology spending can become fragmented and difficult to measure.

Scope should be practical and visible. Define which suppliers, logistics partners, plants, systems, and regions are included. Then map decision rights across procurement, operations, finance, compliance, and sustainability.

The World Economic Forum reports that supply chains can account for more than 50% of an organization’s greenhouse gas emissions. This makes emissions data a governance concern, not only an environmental initiative. It also shows why scope cannot stop at internal facilities.

Use a simple charter with measurable boundaries. Specify who approves supplier changes, which risks require escalation, and how performance is reviewed. Include service levels, data quality, continuity, labor standards, and emissions metrics. Keep the language operational. “Review quarterly” is weaker than “review supplier disruption exposure every 90 days.” A useful governance model should survive a delayed shipment, a missing data field, or a sudden capacity shortage. It may not work perfectly at first. That is acceptable. Test it with one product category, record the friction, and revise the rules before expanding them.

Map Decision Rights Across the Supply Chain Network

An effective supply chain governance strategy starts by mapping decision rights across the network. Do not assume authority follows job titles. A demand planner may own the forecast, while a regional team controls urgent replenishment. These boundaries must be visible.

Create a decision map for planning, sourcing, production, inventory, transport, and customer service. For each decision, name the accountable role, required contributors, approval limit, and escalation path. For example, a warehouse manager can release emergency stock within a defined threshold. Larger releases require approval from the supply planning lead. Record the decision in a shared system, including the data used and the time of approval. This creates an audit trail and reduces repeated arguments.

The map should also define data rights. Who can change a delivery date? Who validates supplier capacity? Who resolves conflicting inventory records? In practical governance work, unclear data ownership often causes more delays than poor forecasting. Our first decision map looked precise, but it failed during a regional disruption because no role owned customer prioritization. That gap exposed a weakness.

Keep decision rights close to the work, but not without controls. Review the map after major disruptions, missed service targets, or network changes. Ask whether approval steps protected the business or simply slowed it down. Some decisions will remain imperfect. That is acceptable if the risks are understood, documented, and reviewed by qualified leaders.

Establish Governance Policies, Standards, and Controls

How to Build an Effective Supply Chain Governance Strategy

Supply chain governance starts with clear policies, not oversized manuals. Define who approves suppliers, changes specifications, and accepts delivery exceptions. Each policy should name an owner, a review date, and measurable evidence. The 2023 Deloitte Global Chief Procurement Officer Survey reported that 57% of procurement leaders considered digital transformation a high priority. Governance must therefore cover system access, data quality, and automated approvals. Keep the control visible.

Standards convert policy into daily behavior. Set requirements for supplier onboarding, ethical sourcing, cybersecurity, quality, and business continuity. Use one supplier risk scorecard, but allow risk-based escalation. A critical component supplier should face deeper checks than a low-value office supplier. The World Economic Forum’s Global Cybersecurity Outlook 2024 found that 41% of organizations experienced a material cybersecurity incident caused by a third party. That figure makes supplier access a governance issue, not merely an information-technology concern. Require multi-factor authentication, access reviews, and incident notification timelines.

Controls should produce evidence without slowing every purchase. Match purchase orders, receipts, and invoices. Review unusual pricing, split orders, and inactive suppliers monthly. Independent testing should challenge management assumptions. I have seen teams measure policy completion while missing repeated delivery failures. That is a design weakness. Track outcomes too: supplier incidents, corrective-action closure, audit exceptions, and recovery time. The 2023 IBM Cost of a Data Breach Report placed the average breach cost at 4.45 million dollars, reinforcing the value of preventive controls. Still, no framework is perfect. Review failed exceptions honestly, then adjust the policy, standard, or control.

How to Build an Effective Supply Chain Governance Strategy

Establish Governance Policies, Standards, and Controls

Effective supply chain governance depends on clearly documented policies, consistent standards, risk-based supplier classification, regular control testing, and timely issue remediation. The target levels below represent practical governance priorities for building a controlled and accountable supply chain operating model.

Align Performance Metrics, Risk Management, and Accountability

Effective supply chain governance begins with shared performance metrics. Every supplier should understand how results will be measured. Useful measures include delivery accuracy, defect rates, lead-time variation, and recovery speed after disruption. Keep the dashboard small. Too many indicators hide urgent signals.

Our team once rewarded low purchase costs without tracking late deliveries. The result looked efficient on paper but created production delays. We now balance cost with service, quality, inventory exposure, and resilience. Each metric needs a defined owner, calculation method, and review frequency. Data should come from traceable records, not informal estimates. That discipline improves confidence, although data quality still requires regular checking.

Risk management should connect directly to accountability. Maintain a live risk register with probability, business impact, warning signs, and assigned actions. Review critical risks during monthly governance meetings. Escalate missed controls quickly. A supplier may report a capacity concern, while an internal planner may overlook a weak backup plan. Both issues deserve attention. Clear decision rights prevent delays when conditions change. Written action logs also support audits and honest learning.

Accountability must remain practical. Assign one person to each corrective action and set a visible deadline. Managers should question repeated exceptions, not only celebrate target performance. Some measures will prove poorly designed. Change them when evidence demands it. Governance becomes stronger when teams can admit gaps without hiding them.

How to Build an Effective Supply Chain Governance Strategy - Align Performance Metrics, Risk Management, and Accountability
Supply chain governance framework with measurable performance standards, risk controls, decision rights, and review mechanisms.
Governance Dimension Performance Metric Definition and Measurement Method Recommended Target Risk Trigger Accountable Role Review Cadence Required Action
Customer Service On-Time, In-Full Delivery Percentage of customer orders delivered by the confirmed date and in the confirmed quantity. At least 95% Below 90% for two consecutive periods Supply Chain Director Monthly Perform root-cause analysis and approve a corrective action plan with named owners and deadlines.
Demand Planning Forecast Accuracy Forecast accuracy measured using weighted absolute percentage error at the agreed planning horizon. At least 80% at four weeks Below 70% for two consecutive cycles Demand Planning Manager Monthly Review demand assumptions, promotional effects, market signals, and forecast bias.
Inventory Control Inventory Record Accuracy Percentage of sampled inventory records that match the physically verified quantity within the approved tolerance. At least 98% Below 95% or repeated unexplained variances Warehouse Manager Weekly and monthly Increase cycle counts, investigate transaction errors, and reconcile inventory adjustments.
Working Capital Days of Inventory on Hand Average inventory value divided by the relevant cost of sales, multiplied by the number of days in the period. Within approved category-specific budget More than 10% above budget Finance Business Partner Monthly Review excess, obsolete, safety-stock, and replenishment parameters.
Supplier Governance Supplier Corrective Action Closure Percentage of approved supplier corrective actions closed and verified by the agreed due date. At least 95% on time Any critical action overdue by more than 30 days Supplier Quality Manager Monthly Escalate the supplier, validate containment, and determine whether sourcing diversification is required.
Supply Continuity Critical Supplier Risk Assessment Coverage Percentage of critical suppliers with a current assessment covering financial, operational, geographic, cyber, and compliance risks. 100% annually Any critical supplier without a current assessment Chief Procurement Officer Quarterly and annually Complete the assessment, document mitigation plans, and assign an executive risk owner.
Resilience Business Continuity Test Completion Percentage of high-impact supply chain processes with a tested continuity or recovery plan. At least 90% annually A high-impact process fails or lacks a tested plan Business Continuity Lead Quarterly Run a scenario exercise, record recovery gaps, and fund remediation according to risk priority.
Quality and Compliance Nonconformance Rate Number of accepted units or deliveries with verified quality nonconformances divided by total accepted units or deliveries. Below 1.0% Above 2.0% or any critical defect Quality Director Monthly Contain affected material, complete corrective action, and confirm effectiveness through follow-up verification.
Logistics Cost Freight Cost per Shipment Total transportation cost divided by the number of completed shipments, tracked by lane and mode. Within approved budget More than 8% above budget Logistics Manager Monthly Review carrier performance, mode selection, shipment consolidation, and accessorial charges.
Data Governance Master Data Completeness Percentage of active items, suppliers, and locations containing all mandatory planning and execution fields. At least 99% Below 97% or repeated planning errors Data Governance Manager Monthly Correct missing or invalid records, strengthen validation rules, and assign data ownership.
Cyber and Technology Risk Critical System Patch Compliance Percentage of critical supply chain applications and connected assets patched within the approved security window. At least 95% within 30 days Any critical vulnerability outside the approved window Chief Information Security Officer Monthly Apply compensating controls, document exceptions, and escalate unresolved vulnerabilities.
Accountability Action Closure Rate Percentage of governance actions completed by the agreed due date and supported by documented evidence. At least 90% Below 85% for two consecutive reviews Supply Chain Governance Office Monthly Escalate overdue actions, reassign ownership where necessary, and report unresolved issues to the steering committee.
Executive Oversight Risk Decision Documentation Percentage of material supply chain risks with a documented decision, risk owner, treatment plan, and review date. 100% Any material risk without an approved decision Supply Chain Steering Committee Quarterly Record the decision in the risk register and confirm funding, ownership, and escalation thresholds.

Review Governance Outcomes and Improve the Operating Model

How to Build an Effective Supply Chain Governance Strategy

An effective governance strategy must be tested against real operating results. Review delivery reliability, inventory accuracy, supplier responsiveness, and approval cycle times each quarter. Do not rely only on polished dashboards. Walk through a delayed order and trace every decision, handoff, and exception. This reveals whether governance supports work or simply adds meetings. In my experience, teams often measure compliance more carefully than business value. That imbalance deserves attention.

Tips: Use five to seven outcome measures. Assign one accountable owner to each measure. Compare results with the previous quarter, not with an ideal target alone. Ask frontline planners where the operating model slows them down. Their comments may expose problems that reports miss.

Improve the model through controlled adjustments. Clarify decision rights when procurement, operations, and finance share responsibility. Create a simple escalation path for supply shortages and quality concerns. Review committee membership when discussions repeat without decisions. A monthly governance review can examine unresolved actions, root causes, and agreed changes. Keep evidence in one accessible record, including the decision date and expected impact. Not every change will work. That is useful information, if leaders record what failed and why. A practical model becomes stronger when reviews lead to visible changes in roles, workflows, and performance measures.

Go to Top